About NativeAI

A Swiss company with one job: AI security.

NativeAI builds the sovereign security layer between Swiss organizations and the AI they use. Owner-managed, developed in Switzerland and hosted on our own servers in a Swiss datacenter in Lausanne, under Swiss law.

Recognition

Vetted by Switzerland's startup ecosystem.

>>venture>> 2026 · Business & Finance
Top 10 of 451

Selected as one of ten Business & Finance semi-finalists in Switzerland's largest startup competition, from 451 submissions reviewed by 211 jurors. A joint initiative of ETH Zürich, EPFL, McKinsey and Innosuisse.
>>venture>> 2026 · Spotlight Award
Swiss AI, Apertus

Nominated for the Spotlight Award for integrating Apertus, Switzerland's open-source LLM from ETH Zürich, EPFL and CSCS, into NativeAI Guard: sovereign AI governance on sovereign AI infrastructure.

FIT Digital · Digital Grant 2026
Backed by FIT

After dossier review and a pitch before the jury, the Fondation pour l'innovation et la technologie (FIT) supports NativeAI with a FIT Digital Grant. FIT is the Vaud foundation that funds early-stage technology startups.

zünder accelerator
Accelerated in Switzerland

Admitted to and developed at zünder, one of Switzerland's leading startup accelerators, where the feedback confirmed the thesis: Swiss enterprises need a sovereign, purpose-built solution for AI security.

La Forge · EPFL
Incubated at EPFL

Admitted to La Forge, the EPFL Innovation Park incubator for early-stage companies with a connection to EPFL: a network of founders, access to investors and expertise, in the middle of the campus where founder Bernard A. Gütermann graduated.

The company

Owner-managed. By design, not by accident.

NativeAI is owner-managed: owned and run by its founders. No foreign parent company, no hyperscaler dependency, no investor with the power to move your data or our jurisdiction. The people who built NativeAI Guard are the people who answer for it.

That matters in our business more than in most: a security layer is a trust decision. When you route your most sensitive AI traffic through NativeAI Guard, you are trusting a company whose ownership, engineering and infrastructure all sit in the same place, under the same law, answerable to the same people.

OWNERSHIPFounder-owned and founder-run, decisions made in Switzerland
ENGINEERINGDeveloped in Switzerland, 100% Swiss-made, operated in Switzerland
INFRASTRUCTUREOur own servers in a Swiss datacenter in Lausanne, no public cloud
JURISDICTIONSwiss law, end to end, outside the reach of the US Cloud Act
DEPLOYED INHealthcare, banks, insurers, government agencies and critical infrastructure

Our team

The people behind NativeAI.

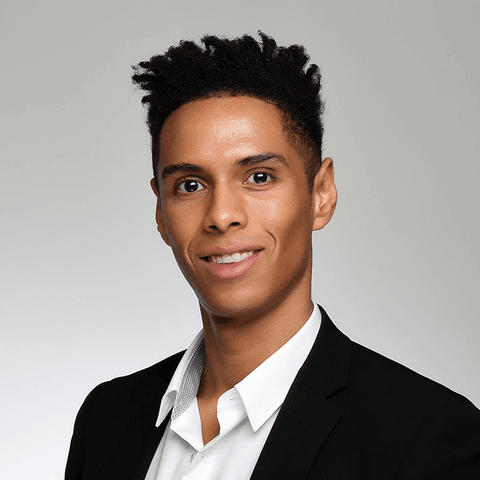
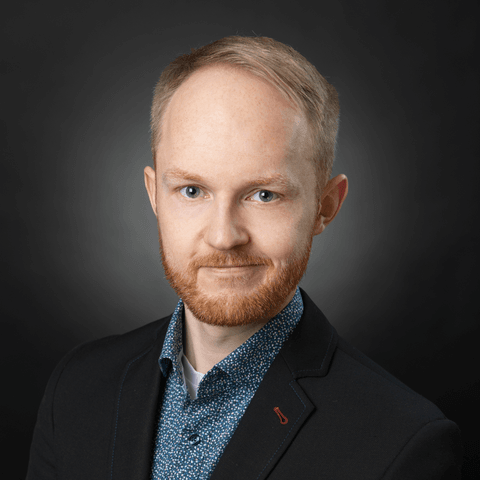
Bernard A. Gütermann
Founder · Product & Engineering · EPFL

Over ten years of experience building secure AI and cloud systems. Bernard designed and built the NativeAI Guard architecture: the browser extension, the policy engine and the proxy layer for agents. He writes or reviews every line of code before it is deployed. Deep expertise in the adversarial AI landscape (jailbreaks, prompt injection, XPIA) and in running the entire infrastructure in-house, with no external dependency.

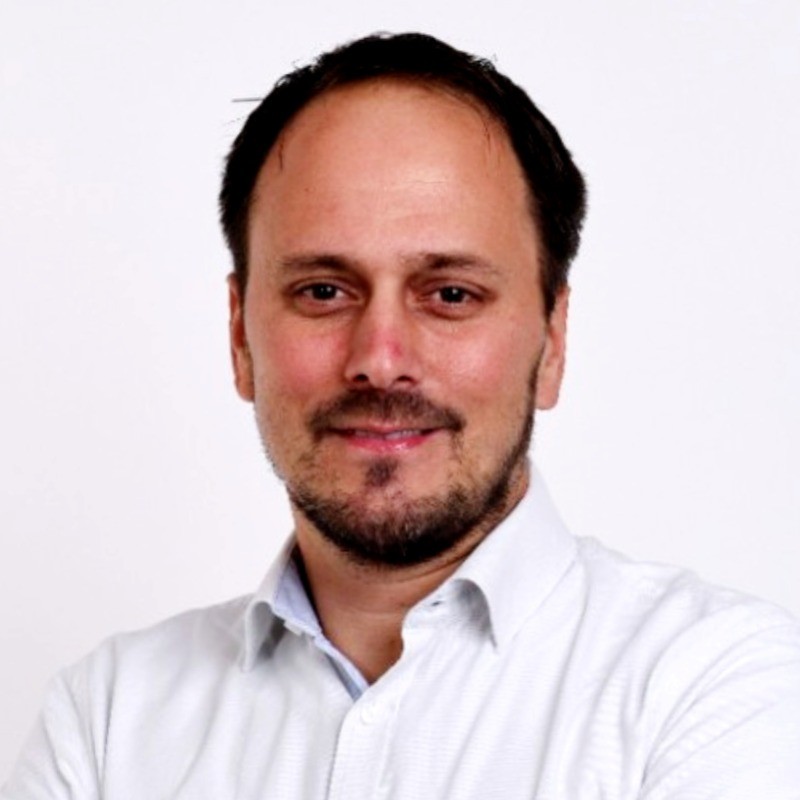
Felix Zeeb
Felix Zeeb
Founder · Customers & Operations

Over eight years working inside large Swiss enterprises across finance, healthcare and the public sector, and knows their realities first-hand: stakeholder committees, procurement cycles, compliance sign-offs. Your counterpart from the first conversation to live operation, so a pilot phase fits your organization instead of working against it.

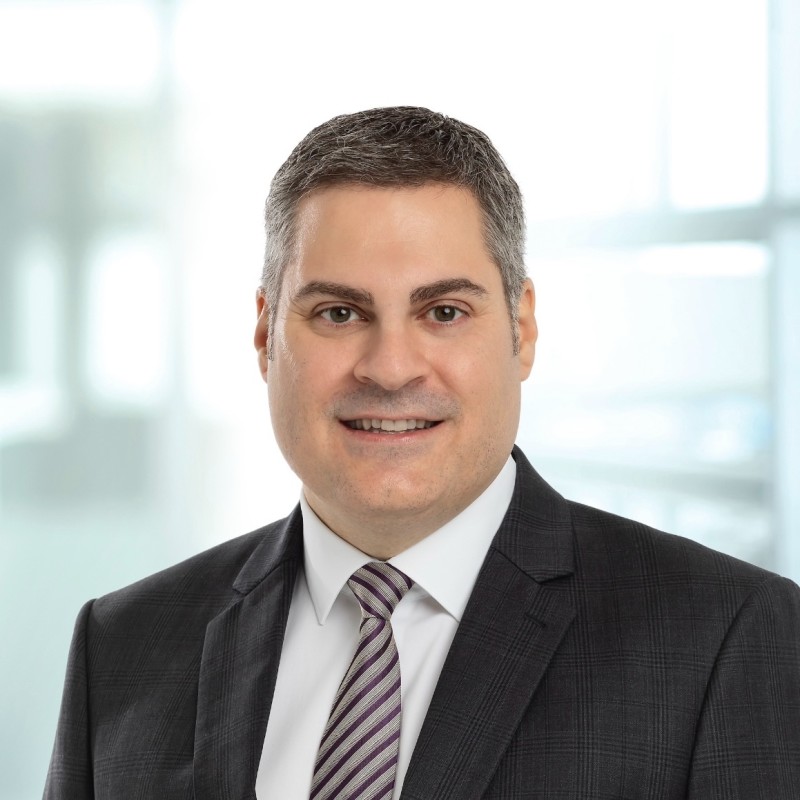
Marc-Etienne Cortesi
Advisor

Former CISO of Baloise and former board member of the Swiss Financial Sector Cyber Security Centre (FS-CSC). He has sat on your side of the table, and makes sure NativeAI Guard holds up to a security review in the Swiss financial sector.

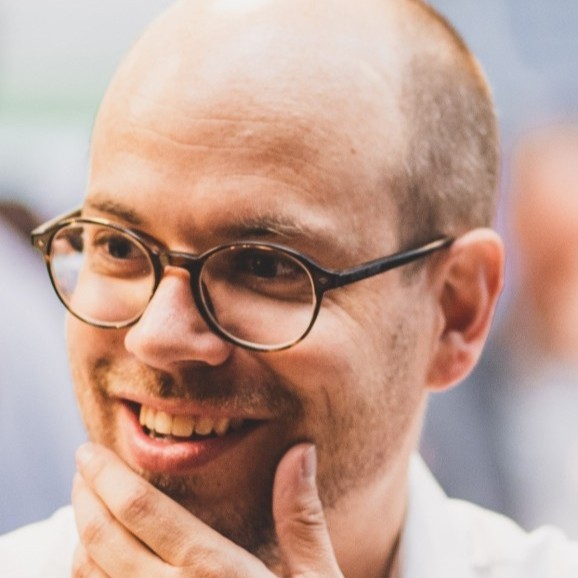
Alexander Bösch
Alexander Bösch
Advisor

Deputy Chief Security Officer of SIX Group, which operates the infrastructure Swiss financial institutions trade and settle on. He reviews our security architecture and our roadmap against the standard a large regulated institution actually applies, and tells us where it would not hold up.

Stefan von Rohr
Stefan von Rohr
Advisor

Co-founder of a Swiss cybersecurity circle where security and IT leaders of Swiss enterprises meet, and startup coach at the zünder accelerator. Those two vantage points give us a direct line to the market: candid feedback that shapes NativeAI Guard around what Swiss enterprises actually need, and a clear read on how to reach the right stakeholders in each organization.

Why we exist

Not a US cloud tool with a Swiss flag on it.

Every organization is adopting AI. Almost none have controls for it. And for Swiss banks, clinics, insurers and public offices, the tools on offer come with a structural problem: they run on infrastructure governed by foreign law (US Cloud Act).

We built NativeAI Guard because sovereign AI governance needs sovereign infrastructure, the entire stack. That is a product decision no one can retrofit, and it is the reason we exist as a Swiss company rather than a Swiss branch office.

Where we work

Based at EPFL Innovation Park.

NativeAI Sàrl is based at the EPFL Innovation Park in Lausanne, the deep-tech hub at the core of the EPFL campus.

The connection is real: co-founder Bernard A. Gütermann is an EPFL alumnus, and our servers run in a nearby datacenter in Lausanne. Being part of this ecosystem keeps us close to the engineers we hire, the researchers we learn from and the Swiss institutions we build for.

NativeAI Sàrl · EPFL Innovation Park · Bâtiment C · 1015 Lausanne · Switzerland

EPFL INNOVATION PARK · LAUSANNE

Common questions

Frequently asked questions

What is your certification status?

ISO 27001 is in active preparation: the management system is built and running, and certification has not yet been awarded. We hold no SOC 2 Type II report today, and we will undergo the audit whenever a customer requires it as part of their own assurance process. If your vendor process needs the current state in writing, including the ISMS scope and the evidence behind it, we are happy to share it with you.

You are a small Swiss team, and large international vendors are pushing into this market. Why you?

Asked directly by a cantonal CISO, so here is the direct answer. We cannot outspend a platform vendor, and we do not try to. What a platform vendor structurally cannot offer is digital sovereignty: servers, software and law entirely in Switzerland, outside the reach of the US Cloud Act. What you get from us instead is a partnership. The people who built the product are in the room during your security review, and the requirements you raise go into the product: more than one capability in NativeAI Guard today exists because a Swiss security team told us they needed it. We are here to give you the security solution you need, not the one we decided to ship this quarter. Whether you use our Swiss SaaS or run the product on your own infrastructure, you stay in control: the policies are yours, the audit logs are yours and exportable at any time, and you can move from one deployment mode to the other without changing product. The relationship holds because the work is right, not because lock-in forces it. We are owner-managed, so the roadmap answers to customers rather than to investors. A head of IT security at a Swiss bank put the rest better than we could: if nobody works with Swiss startups, Swiss alternatives never come into existence.

Will you have access to our systems or our data?

No. We do not require access to your internal systems, and support work does not create a route into them. Where a customer explicitly authorizes access for a specific agreed purpose, that authorization is in writing and limited in scope. Several of our customers made this a mandatory governance requirement before signing, and we would rather have it in the contract than leave it as a promise.

Where does it actually run, and who owns the hardware?

On our own servers in a datacenter in Lausanne. Not a hyperscaler region with a Swiss label, not a reseller arrangement: servers we own and operate, under Swiss law. That is exactly what puts the processing outside the reach of the US CLOUD Act, and it is the question customers in regulated sectors and international organizations usually ask.

Can we start on your infrastructure and move to on-premises later?

Yes, and several customers plan exactly that. The same product runs in both deployment modes, with the same detection engine and the same policies. Moving is therefore an operational matter, not a migration to a different product. Starting on Swiss SaaS shortens the path to a solid result; moving to on-premises later is a decision you can take once the value is proven.

We have evaluated Microsoft Purview. It integrates natively with our M365 stack, it is backed by a trillion-dollar company, and frankly, we have never heard of NativeAI. Why should we take the risk with a startup?

Four points on the product, then the real question. First, sovereignty: Purview runs on Microsoft infrastructure, under US law; NativeAI Guard runs on our own servers in Switzerland, outside the reach of the US Cloud Act. No vendor with a US parent company can replicate that, whatever the budget. Second, coverage: Purview protects your M365 perimeter, but ChatGPT, Claude, Gemini and DeepL run outside it, exactly where most employees actually paste data today. Third, effort: Purview needs classification trees and a labeling project before it takes effect; our detection reads content semantically and starts with a working rule set per industry. Fourth, cost: our pricing is a fixed amount per user per month, plannable for the annual budget, not usage-based like Purview's shadow-AI DLP. The real question, though, is a different one: what if NativeAI is no longer around? Three answers. First, the pilot phase: clearly limited scope and duration, you test with a small group, see the result, no long-term commitment. Your risk is limited from the start. Second, the architecture: NativeAI Guard runs inline as a proxy; switch it off and your systems work exactly as before. No migration, no data stuck in our platform, no dependency. Third: on request, we include a source code escrow in the contract, if that is relevant for your risk committee.

Meet the people of NativeAI.

A demo with NativeAI is a conversation with the founders and engineers, no sales team in between.